Remote compliance jobs span governance, risk, and compliance (GRC), financial crimes (AML/KYC), privacy, vendor risk, and product-compliance partnerships in fintech and SaaS. Employers hire for judgment under regulation, audit readiness, and clear writing, not for buzzword stacking. This guide maps role families, skills that transfer, where remote openings appear, and how to present adjacent experience if you are changing careers.
This page was reviewed on September 30, 2026.
TL;DR
- Remote compliance work is common in fintech, payments, and distributed SaaS, but residency and travel-for-audit rules still apply.
- Match the sub-domain: AML/KYC, UDAAP/consumer, privacy, SOC 2/ISO program ops, or vendor due diligence.
- Proof beats adjectives: policies authored, audits supported, issues tracked to closure, training delivered.
- Career changers from audit, legal ops, risk, banking ops, or quality can transfer if they name frameworks and artifacts.
- Use remote boards plus LinkedIn alerts, then verify employer entity and exam/travel expectations.
Remote compliance role map
| Title cluster | Typical ownership | Remote notes |
|---|---|---|
| Compliance analyst / generalist | Recurring controls, reviews, partner questionnaires | Often US-remote with state limits |
| AML / financial crimes | Monitoring, SAR workflows, KYC/KYB | May require licensing entity residency |
| Privacy / data protection | DPIAs, vendor privacy, requests handling | Cross-timezone collaboration common |
| GRC / infosec compliance | SOC 2, ISO, control testing, evidence | Partners with security engineering |
| Compliance manager / head | Program design, exams, leadership | Travel for regulators or offsites possible |
| Sales / product compliance | Marketing review, feature gating | Embedded with GTM or product |
Fintech postings frequently cite BSA/AML, KYC, UDAAP, Reg E/Z, GLBA, or CFPB guidance. Enterprise GRC roles cite SOC 2, ISO 27001, NIST-inspired control catalogs, or industry rules. Read the regulation list before you claim fit.
O*NET and labor references help with occupation framing for compliance officers (O*NET OnLine); open specific codes in a browser when researching adjacent titles. SHRM publishes people and workplace compliance context useful for ethics and employment-adjacent programs (SHRM).
Skills employers screen for
- Framework literacy: enough to map a control to evidence without bluffing.
- Issue management: finding, severity, owner, due date, closure proof.
- Stakeholder writing: policies, audit responses, executive summaries.
- Vendor and partner diligence: questionnaires, residual risk, follow-ups.
- Product partnership: reviewing features before launch without blocking needlessly.
- Tooling comfort: GRC platforms, ticketing, and monitoring tools named in the JD.
| Evidence type | Example you can list |
|---|---|
| Audit support | Gathered evidence packs for a named framework cycle |
| Policy | Authored or revised an acceptable-use or complaints policy |
| Monitoring | Triaged alerts under a documented playbook |
| Training | Delivered compliance awareness modules |
| Cross-functional | Partnered with engineering or support on a control gap |
Avoid inventing exam outcomes or “reduced risk by X%” without a baseline you can explain.
Where to find remote compliance jobs
| Source | Best use |
|---|---|
| Title + remote filter + fintech/SaaS company follows | |
| Indeed | Volume across industries |
| FlexJobs / Remotive-style boards | Curated remote discovery when available |
| Wellfound | Startup compliance and first GRC hires |
| Company career pages | Regulated product companies’ source of truth |
Use the filters and scam checks in remote job boards. Startup compliance openings also appear via startup job boards patterns, though many GRC roles still prefer candidates with prior regulated-industry exposure.
Remote eligibility checklist
- Country or US-state residency limits
- Required overlap with legal/finance headquarters hours
- Annual offsites or exam travel
- Employer of record vs W-2 entity
- Licensing or registration implications for financial products
Career change into remote compliance
People move in from banking operations, internal audit, quality, legal operations, IT audit, customer support in regulated products, and security GRC. If you are changing later in your career, pair this page with career change at 40 and refresh discoverability using LinkedIn profile tips.
Transfer story formula: current domain expertise → regulated process you already ran → compliance artifact you can show → target title language from five postings.
Illustrative (not a promise): a banking ops lead who owned KYC escalation queues reframes as “AML operations → compliance analyst,” highlighting documented playbooks and audit samples rather than “passionate about compliance.”
Resume, LinkedIn, and interview notes
- Headline: “Compliance Analyst | AML & vendor diligence | Fintech program support” (only if accurate).
- Prefer framework nouns and artifact nouns over soft skills.
- Interviewers often ask: how you handled an ambiguous control, how you partnered with product, and how you prioritize when everything is “urgent.”
- Bring one story about pushing back constructively and one about closing an issue with evidence.
Robert Half and similar career publishers discuss compliance and risk hiring trends at a high level (Robert Half); treat salary blogs as directional and confirm with current offers in your market (Payscale can help you triangulate ranges without treating any page as a quote).
Sub-domain deep dive: what “good” looks like
AML and financial crimes
Expect transaction monitoring workflows, escalation judgment, KYC/KYB evidence quality, and comfort with false-positive burden. Interviews often probe how you document decisions and when you escalate. Remote AML roles frequently require residency in licensed jurisdictions.
Privacy
Expect data-subject requests, vendor assessments, DPIA-style analysis, and partnership with engineering on retention and access. Strong candidates show calm writing under incomplete facts.
Infosec GRC / SOC 2 style programs
Expect control ownership mapping, evidence collection cadence, exception handling, and security questionnaire responses. Pairing with engineering respectfully matters as much as framework trivia.
Consumer compliance / marketing review
Expect UDAAP-minded review of product and marketing claims, complaints handling, and audit support. Fintech and lending product companies hire heavily here.
Building evidence when you lack the exact title
If your current title is operations, support, audit, or risk, invent nothing. Extract artifacts:
- A recurring control you already execute (reconciliations, access reviews, partner onboarding packs).
- A policy or SOP you improved.
- An audit or partner request you supported with evidence.
- A cross-functional escalation you documented cleanly.
Rewrite those as compliance-relevant bullets. Then apply to analyst roles that match the artifact family, not only to glamorous “Head of Compliance” posts. For later-career pivots, combine this with career change at 40 pacing: fewer, better applications with sharper proof.
Remote collaboration habits that show up in interviews
Distributed compliance teams live on tickets, shared drives, and meeting notes. Interviewers may ask how you manage deadlines across timezones, how you prepare for an audit week, and how you push back on a launch without becoming a blocker. Prepare one story for each. Mention tools only when you used them; name-dropping a GRC platform you never touched backfires.
Refresh discoverability with LinkedIn profile tips: headline that names the compliance lane, About section that lists frameworks honestly, and featured samples only when shareable.
Weekly search system
| Action | Cadence |
|---|---|
| LinkedIn + board alerts | Daily skim, 20 minutes |
| Employer-page verification | Before every tailored application |
| Artifact folder update | Weekly |
| Informational chat with a compliance practitioner | Biweekly if available |
| Application batch | 3–5 high-fit roles per week |
Quality beats spray-and-pray. Regulated employers notice generic cover letters that confuse AML with SOC 2.
Sample week for a remote compliance analyst
| Block | Example work |
|---|---|
| Morning deep work | Evidence requests, policy edits, questionnaire answers |
| Midday syncs | Product review, risk committee prep, vendor calls |
| Afternoon | Issue tracking hygiene, training materials, audit follow-ups |
| Friday | Metrics snapshot for leadership: open issues, overdue evidence, upcoming exams |
Remote success looks boring on purpose: dated owners, clear statuses, and clean handoffs. If you cannot describe your personal system in an interview, invent one on paper before you apply. Hiring managers in regulated companies fear silent backlog more than imperfect framework trivia.
Offer and background-check expectations
Compliance roles may include stricter background checks, conflict-of-interest questionnaires, and confidentiality agreements. Ask what the timeline looks like after verbal offer. Do not treat a verbal as employment until paperwork completes. Keep other applications warm. For general search hygiene across remote functions, stay disciplined with remote job boards.
Mistakes that stall compliance interviews
- Claiming frameworks you only read about once
- Speaking only in tools instead of decisions and evidence
- Ignoring residency and travel questions until late stages
- Treating product partners as adversaries in your stories
- Submitting the same resume to privacy and AML roles without retargeting
Fix these before the next batch of applications. A thinner, accurate profile beats a broad, fuzzy one when auditors and hiring managers share similar skepticism.
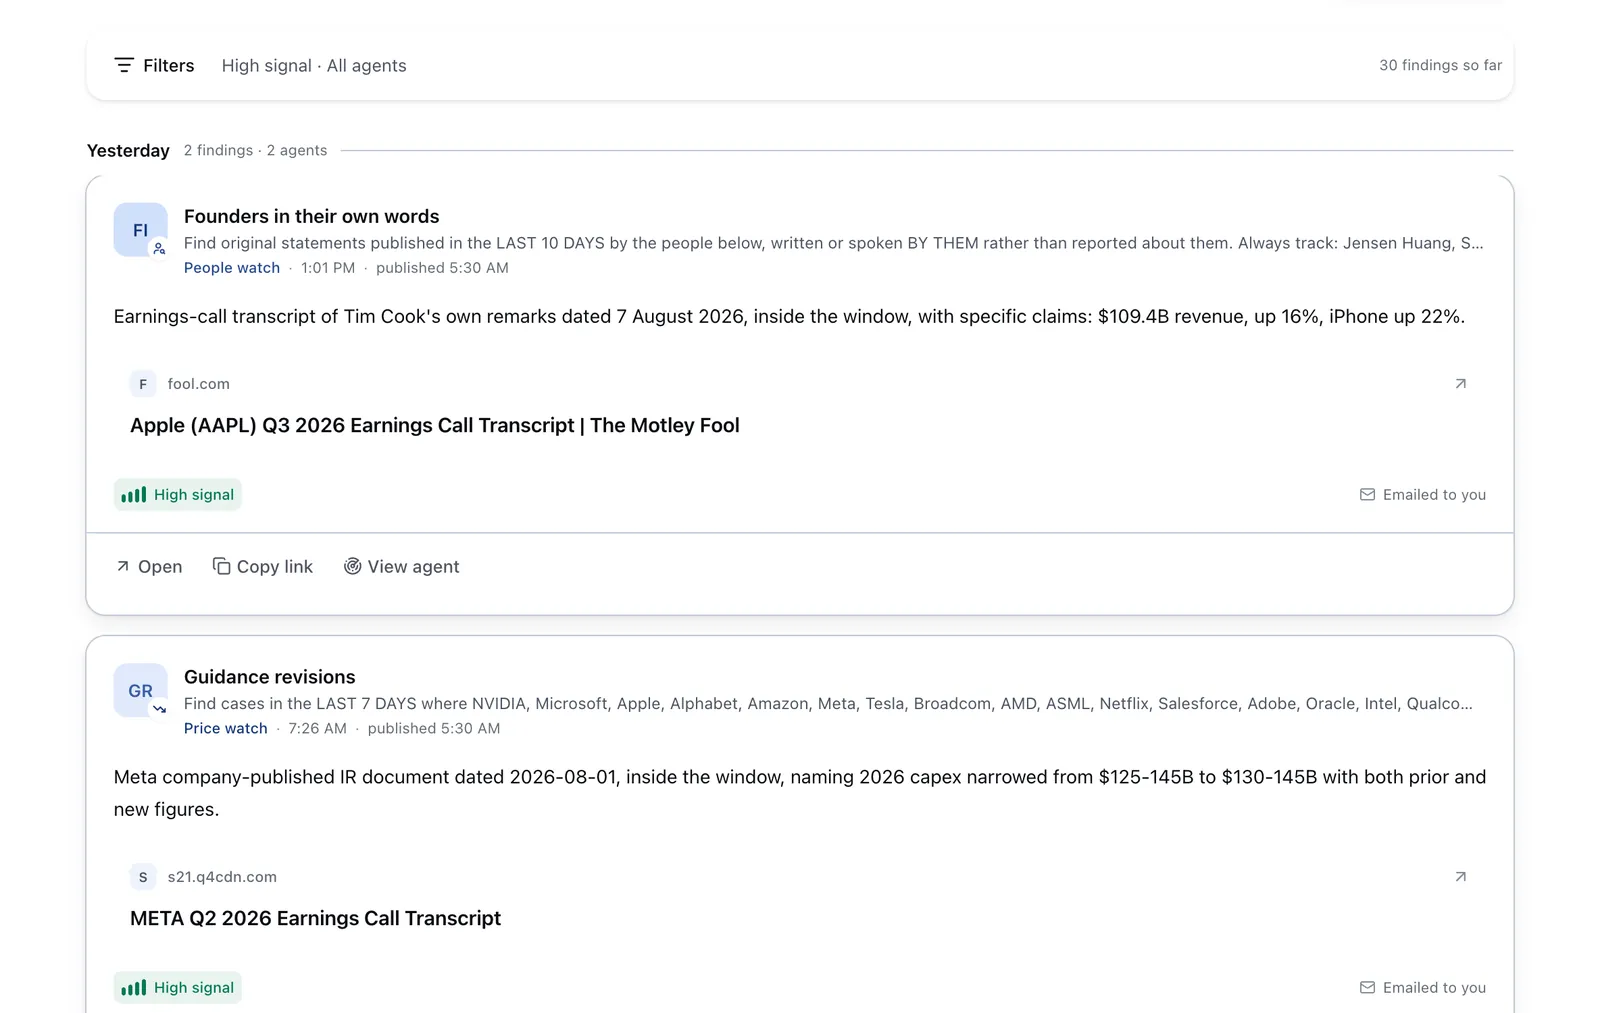
Run it on Parlel
Keep a compliance-focused watch and a profile that names frameworks you can defend.
agent: compliance_remote_watch
keywords: compliance analyst, GRC, AML, KYC, privacy
filters: remote, past_14_days
digest: thursday_17:00
fields: company, regulation_keywords, location_rule, travel_note
profile.skills: aml, kyc, soc2, policy_writing, vendor_risk
Digest shape: { company, role, location_rule, regulation_keywords, verify_careers_page }. Explore /jobs and keep your public profile aligned with the sub-domain you want (AML vs privacy vs infosec GRC).
Keep reading
Frequently asked questions
Are compliance jobs remote-friendly?
Many analyst and specialist roles are remote or hybrid, especially in fintech and SaaS. Leadership and exam-heavy roles may require travel or regional residency.
Do I need a law degree for compliance jobs?
Usually no for analyst roles. Legal degrees help for some counsel-adjacent paths; most operational compliance roles value domain experience and artifacts more.
What certifications help?
Credentials such as CAMS (AML), CIPP (privacy), or CCEP (ethics/compliance) can support screening when paired with real work. They are not universal requirements.
Can I move from IT audit into GRC compliance?
Yes, that is a common path. Emphasize control testing, evidence quality, and stakeholder communication.
How do I avoid fake remote compliance listings?
Verify the company domain, never pay for placement, and be cautious with interviews only on messaging apps. Cross-check the role on the employer site.
Is startup compliance different from bank compliance?
Startups often need builders who create lightweight programs and partner with product. Banks may have heavier procedures and clearer role boundaries. Read the first-90-days expectations carefully.